1 · It runs every day
A scheduled task runs in the early hours and goes through the active categories.
Risk, identity, incident response and compliance.
Spyware vendors are exploiting targeted ad bidding in the digital ecosystem to identify and track individuals and organizations of interest.
Read the entry →Researchers say attackers authenticated into Microsoft 365 tenants using ConnectWise credentials; ConnectWise says customer impact remains …
Read →Copyright takedown requests tied to OnlyFans and other adult content creators are revealing how attackers exploit vulnerable university and…
Read → Cybersecurity
Organizations that run open-weight AI models on their own infrastructure may have to supply safety and security controls that an AI provide…
Read → Cybersecurity
Microsoft accounted for 33% of brand impersonation attempts tracked by Check Point Research in the third quarter of 2026, up from 23% in th…
Read → Cybersecurity
This summer, the White House rolled out the Gold Eagle Initiative, billed as an “unprecedented” effort to coordinate cybersecurity vulnerab…
Read →Bearer CLI is a free static application security testing (SAST) tool that scans source code for vulnerabilities and prioritizes them by the…
Read →Ivanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
Read →Companies are increasingly discovering that the challenge with AI is no longer adoption, but execution.
Read → Cybersecurity
IntroductionSupply chain attacks on package registries have grown in volume and sophistication [1]...
Read →The shocking arrest of a well-known ransomware negotiator reveals the critical need for vendor program oversight.
Read → Cybersecurity
Attackers are breaking into business email accounts with short messages asking whether a company can quote on an upcoming project, the kind…
Read → Cybersecurity
Andrew Martin discusses why AI security is fundamentally tied to Kubernetes security. He shares insights into the evolving AI threat landsc…
Read →
Cybersecurity
Andrew Martin discusses why AI security is fundamentally tied to Kubernetes security. He shares insights into the evolving AI threat landsc…
Read → Cybersecurity
Arch Linux users who mistyped yay or paru while installing the package helpers from the Arch User Repository (AUR) may have given a strange…
Read → Cybersecurity
Software supply chain security company Chainguard has announced two beta products for running and testing code written by developers and AI…
Read → Cybersecurity
Current security procedures for training AI models are inadequate, hundreds of AI researchers have warned governments and the AI community.…
Read → Cybersecurity
Although the Jev model rolled out last month by TypeSafe claims to have significant advantages over traditional LLMs, a security report pub…
Read →The event closed in Toronto last week, with experts sharing critical perspectives on emerging risks, drawing record attendance and marking …
Read →Built from decades of threat intelligence research, the new resource explains scams from the victims' perspective and tracks emerging forms…
Read →Don't buy the hype! AI has been dumbing down cyberattacks, and serious threat actors are barely touching it.
Read → Cybersecurity
Put native GitHub features to work to review outside collaborator access and archive stale repositories. The post Staying Evergreen: How we…
Read →Organizations need to move away from vendor-assigned, theoretical scores toward real exploit data specific to their environments.
Read →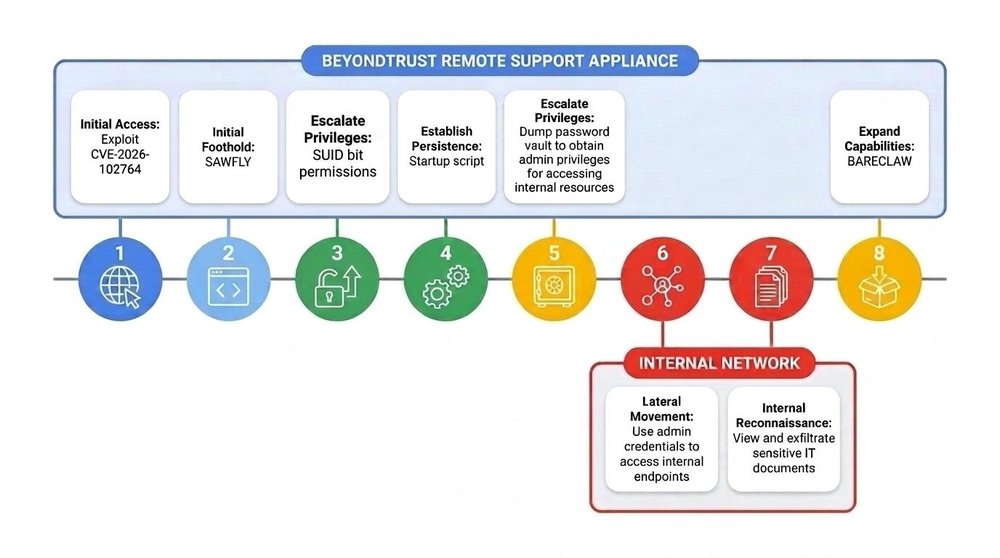 Cybersecurity
Written by: Jayson Frost, Bryce Greathouse, Brian Meyer, John Palmisano, Rajesh Rajeshirke, Steve Rasch, John Wolfram Introduction On Octob…
Read → Cybersecurity
Spring Authorization Server now lives inside Spring Security 7 under the same Maven coordinates, so the upgrade is a version bump. This ser…
Read → Cybersecurity
I’ve spent more than 20 years running IT and security for organizations across California and around the country. Over that time, my team h…
Read →CVE-2026-104935, a high-severity authentication bypass + RCE vulnerability, was only partially discovered and patched in July, leaving an o…
Read →A sprawling cybercrime marketplace supplied cloud infrastructure and phishing kits that helped fuel more than 1 billion phishing messages w…
Read →A bug in Claude Code Desktop's preview pane can allow adversaries to quietly steal credentials from developers, including SSH private keys,…
Read → Cybersecurity
Enterprises have historically built separate network and security architectures, but this separation is becoming increasingly difficult to …
Read →A scheduled process prepares the entries for each category every day; I review them, edit them and add my own from the administration console.
A scheduled task runs in the early hours and goes through the active categories.
Title, summary and analysis, with the source cited and the original link always visible.
It takes the cover image from the source or a stock image with a free-use license.
From the console I approve, correct or write my own entries and articles.
An open conversation to share knowledge. Messages reach my console and I reply from there.
Pick the day and time that work for you. Thirty minutes, no sales pitch.
For a video call, just ask for one here and I'll send you the session link.